Attack Map
Visualizing cyber threats in real time.
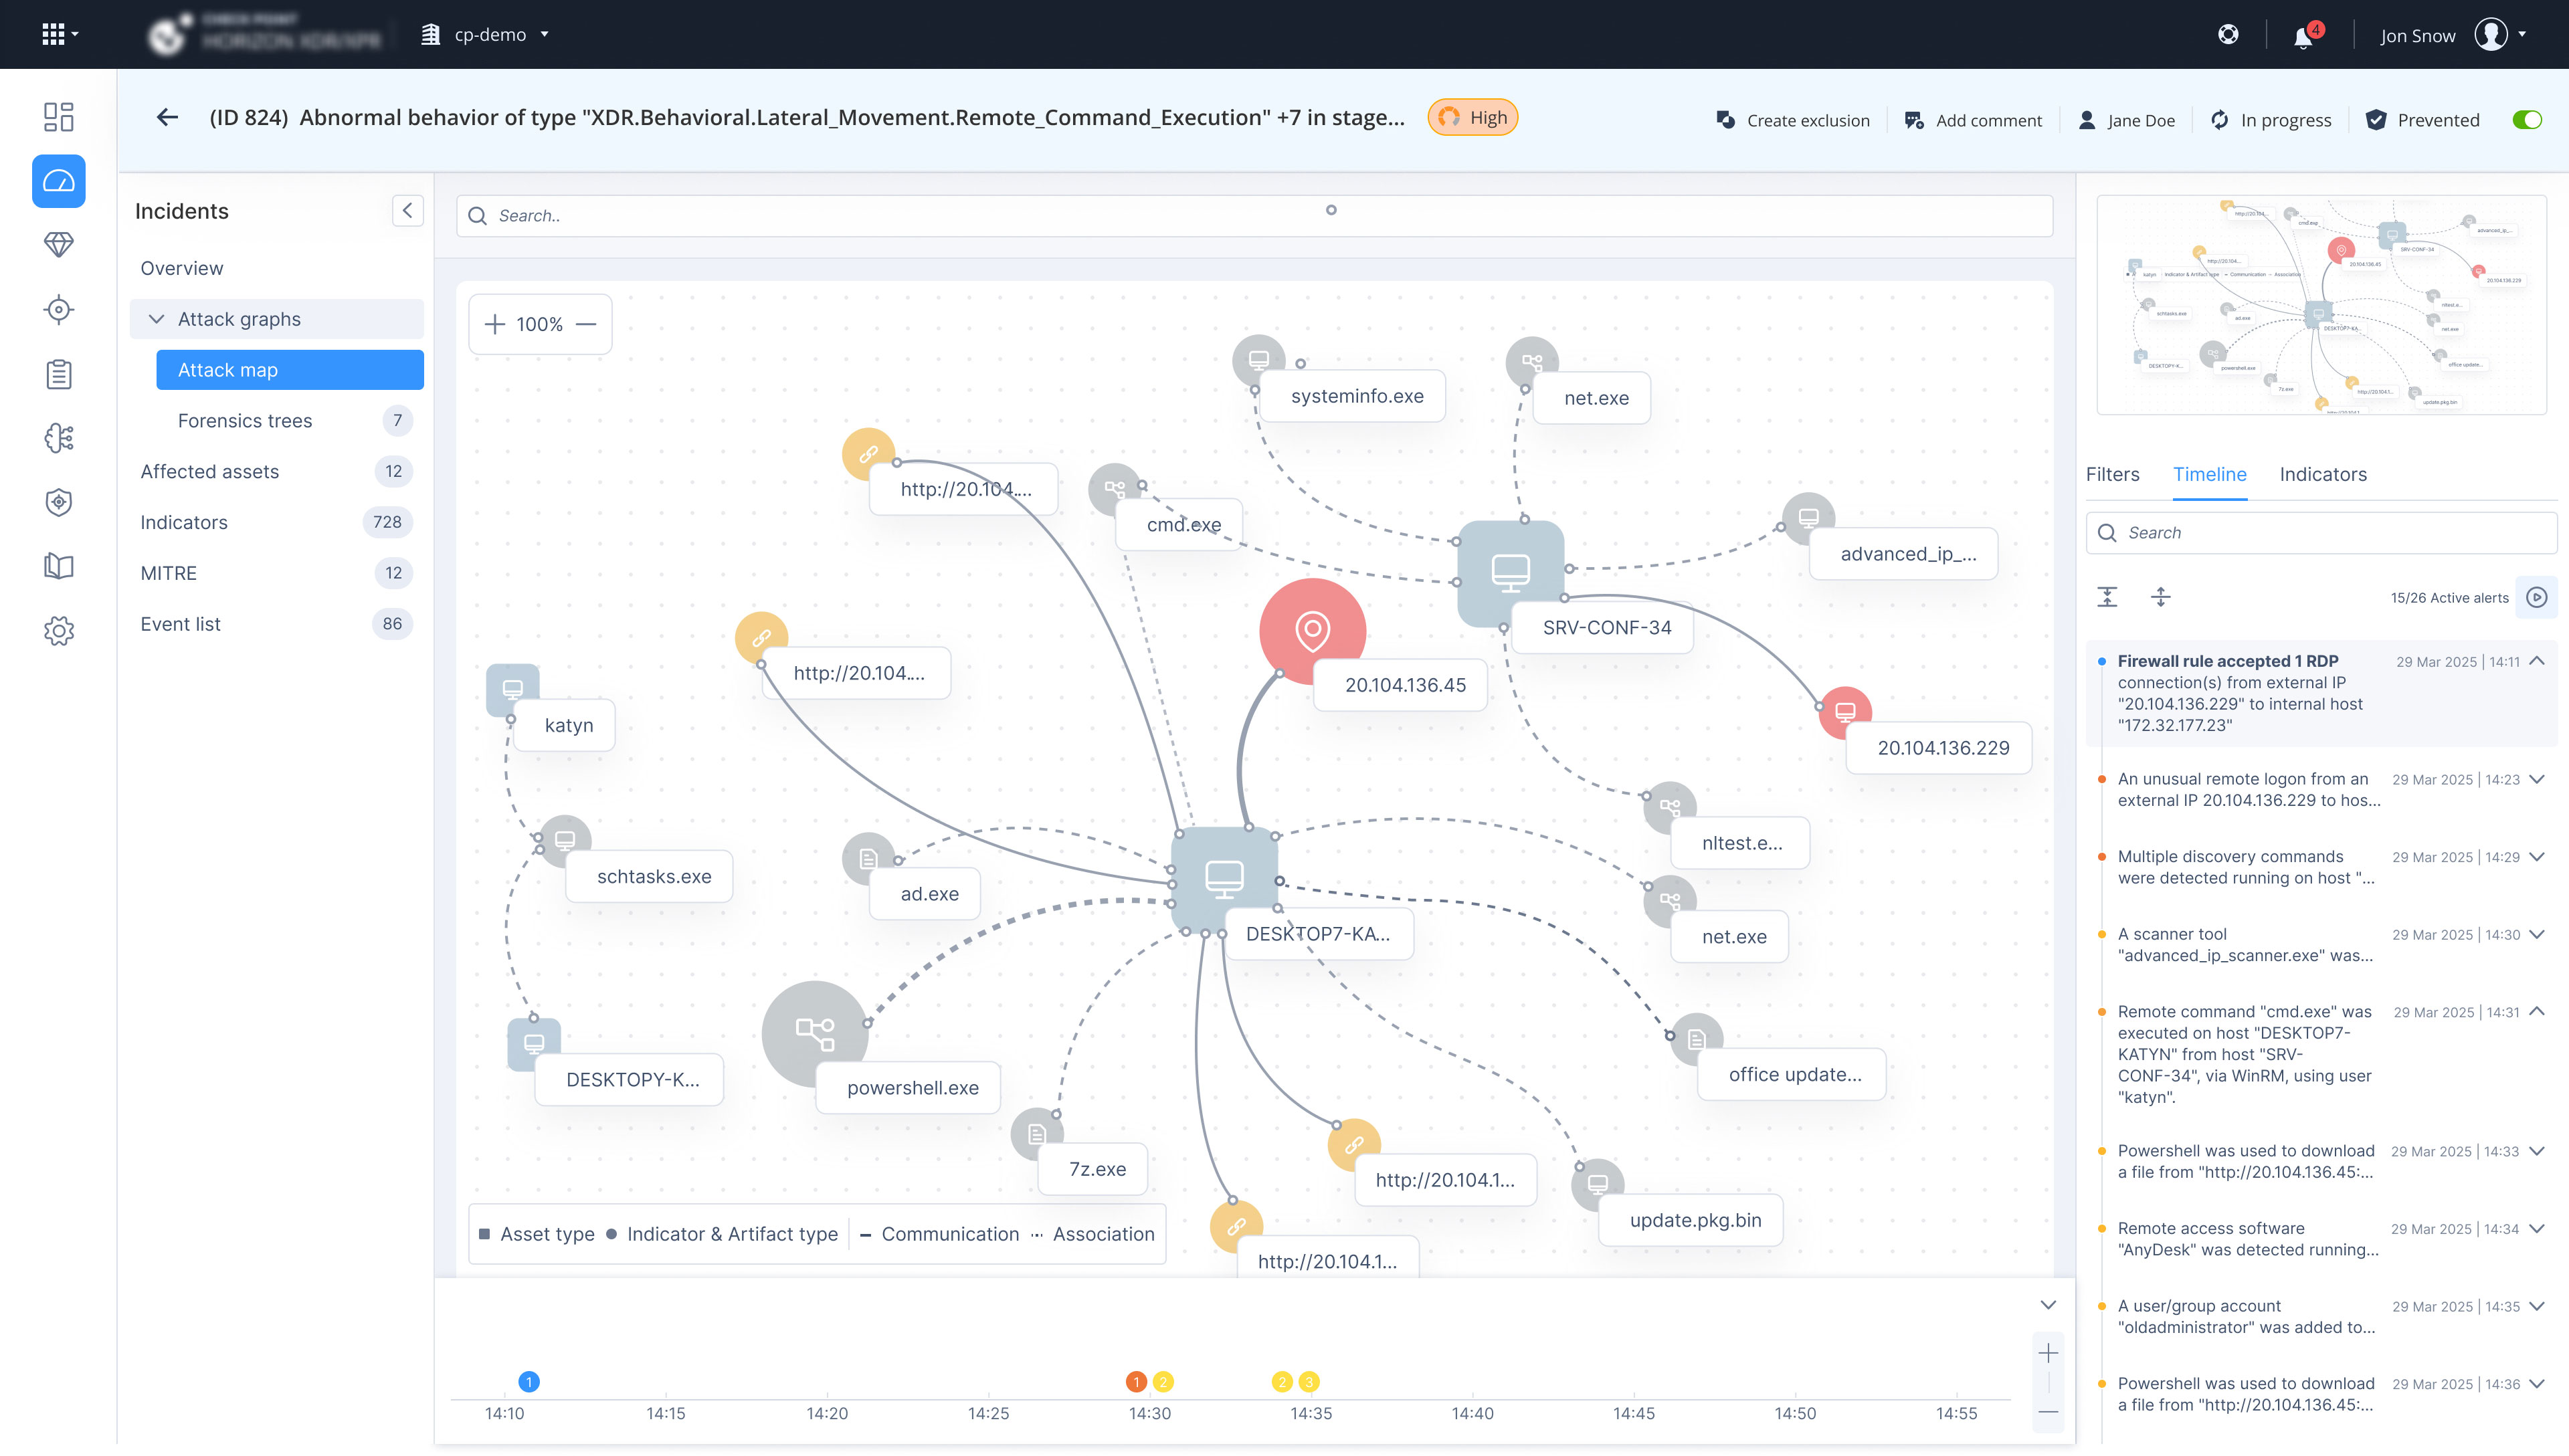
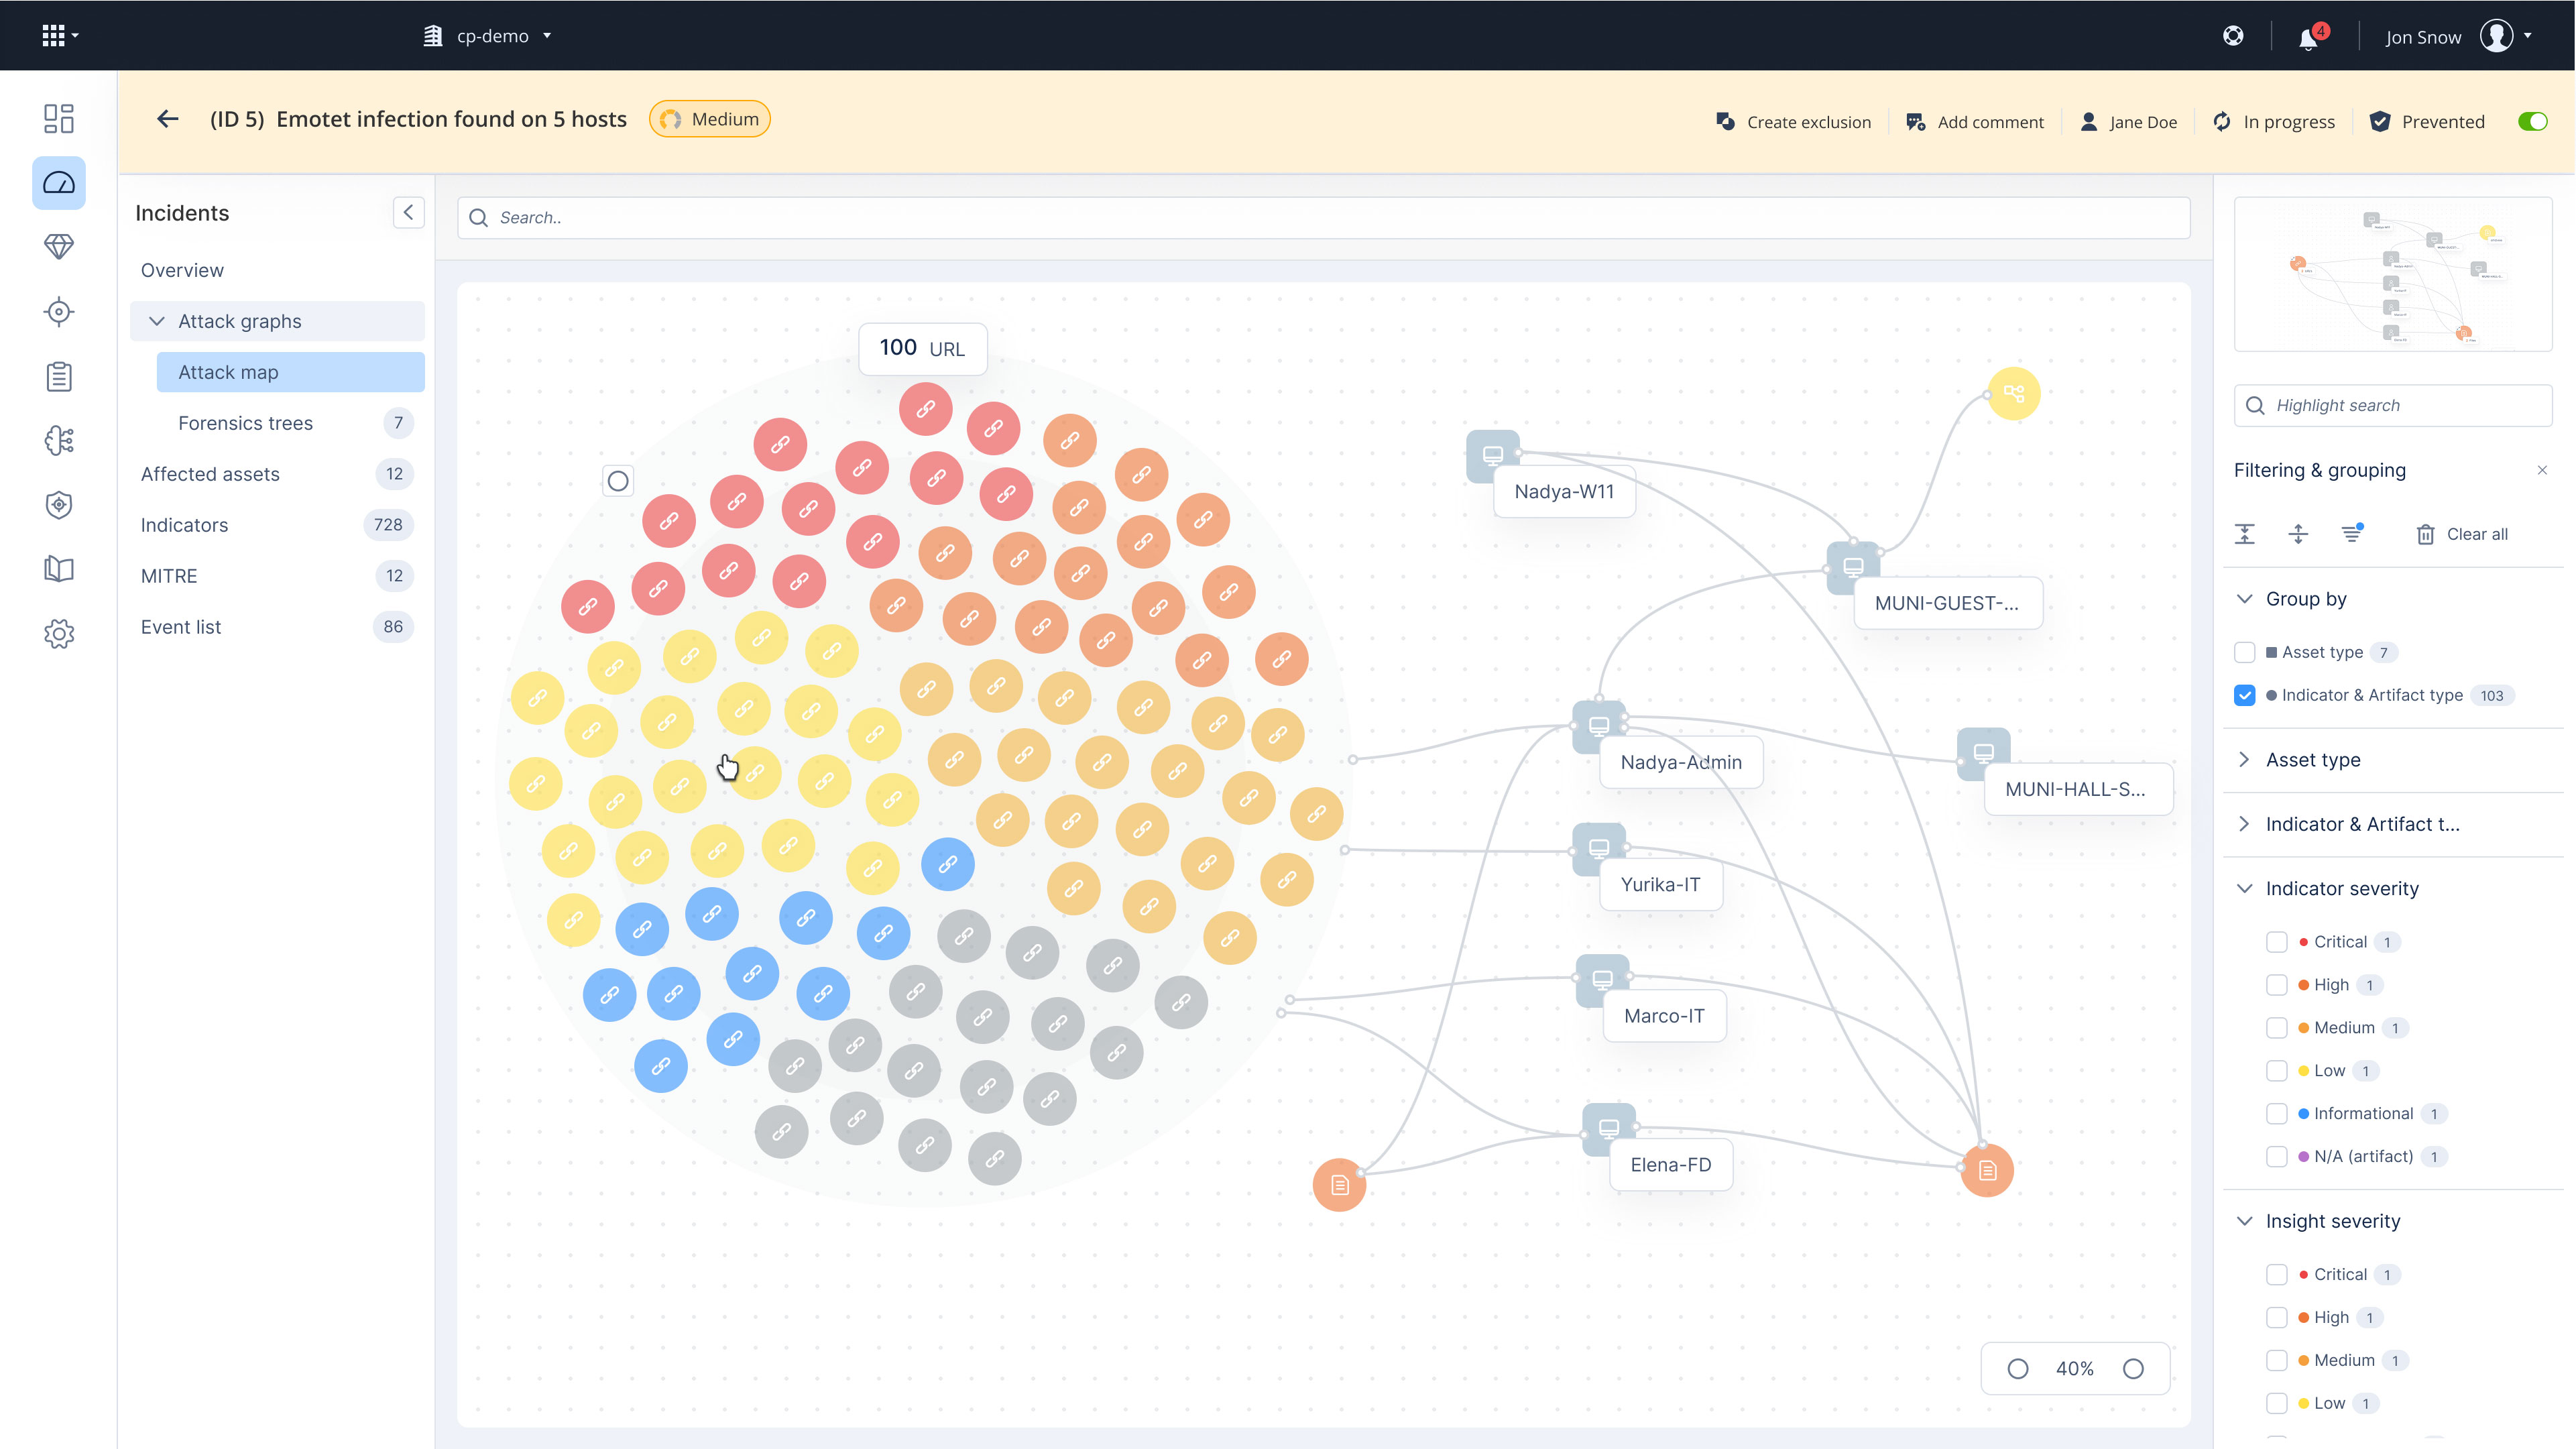
Open the map → Scan relationships → Identify entities → Group when helpful → Inspect a group → Continue investigating
Context & contribution
Helping SOC analysts understand relationships and follow the sequence of an attack.
User goal
Give SOC analysts a clear path from a crowded map to the entities and relationships that matter to an investigation.
User flow
- 01
Open the map
Start with the entities involved in the attack.
- 02
Scan relationships
Follow the connections between assets and indicators.
- 03
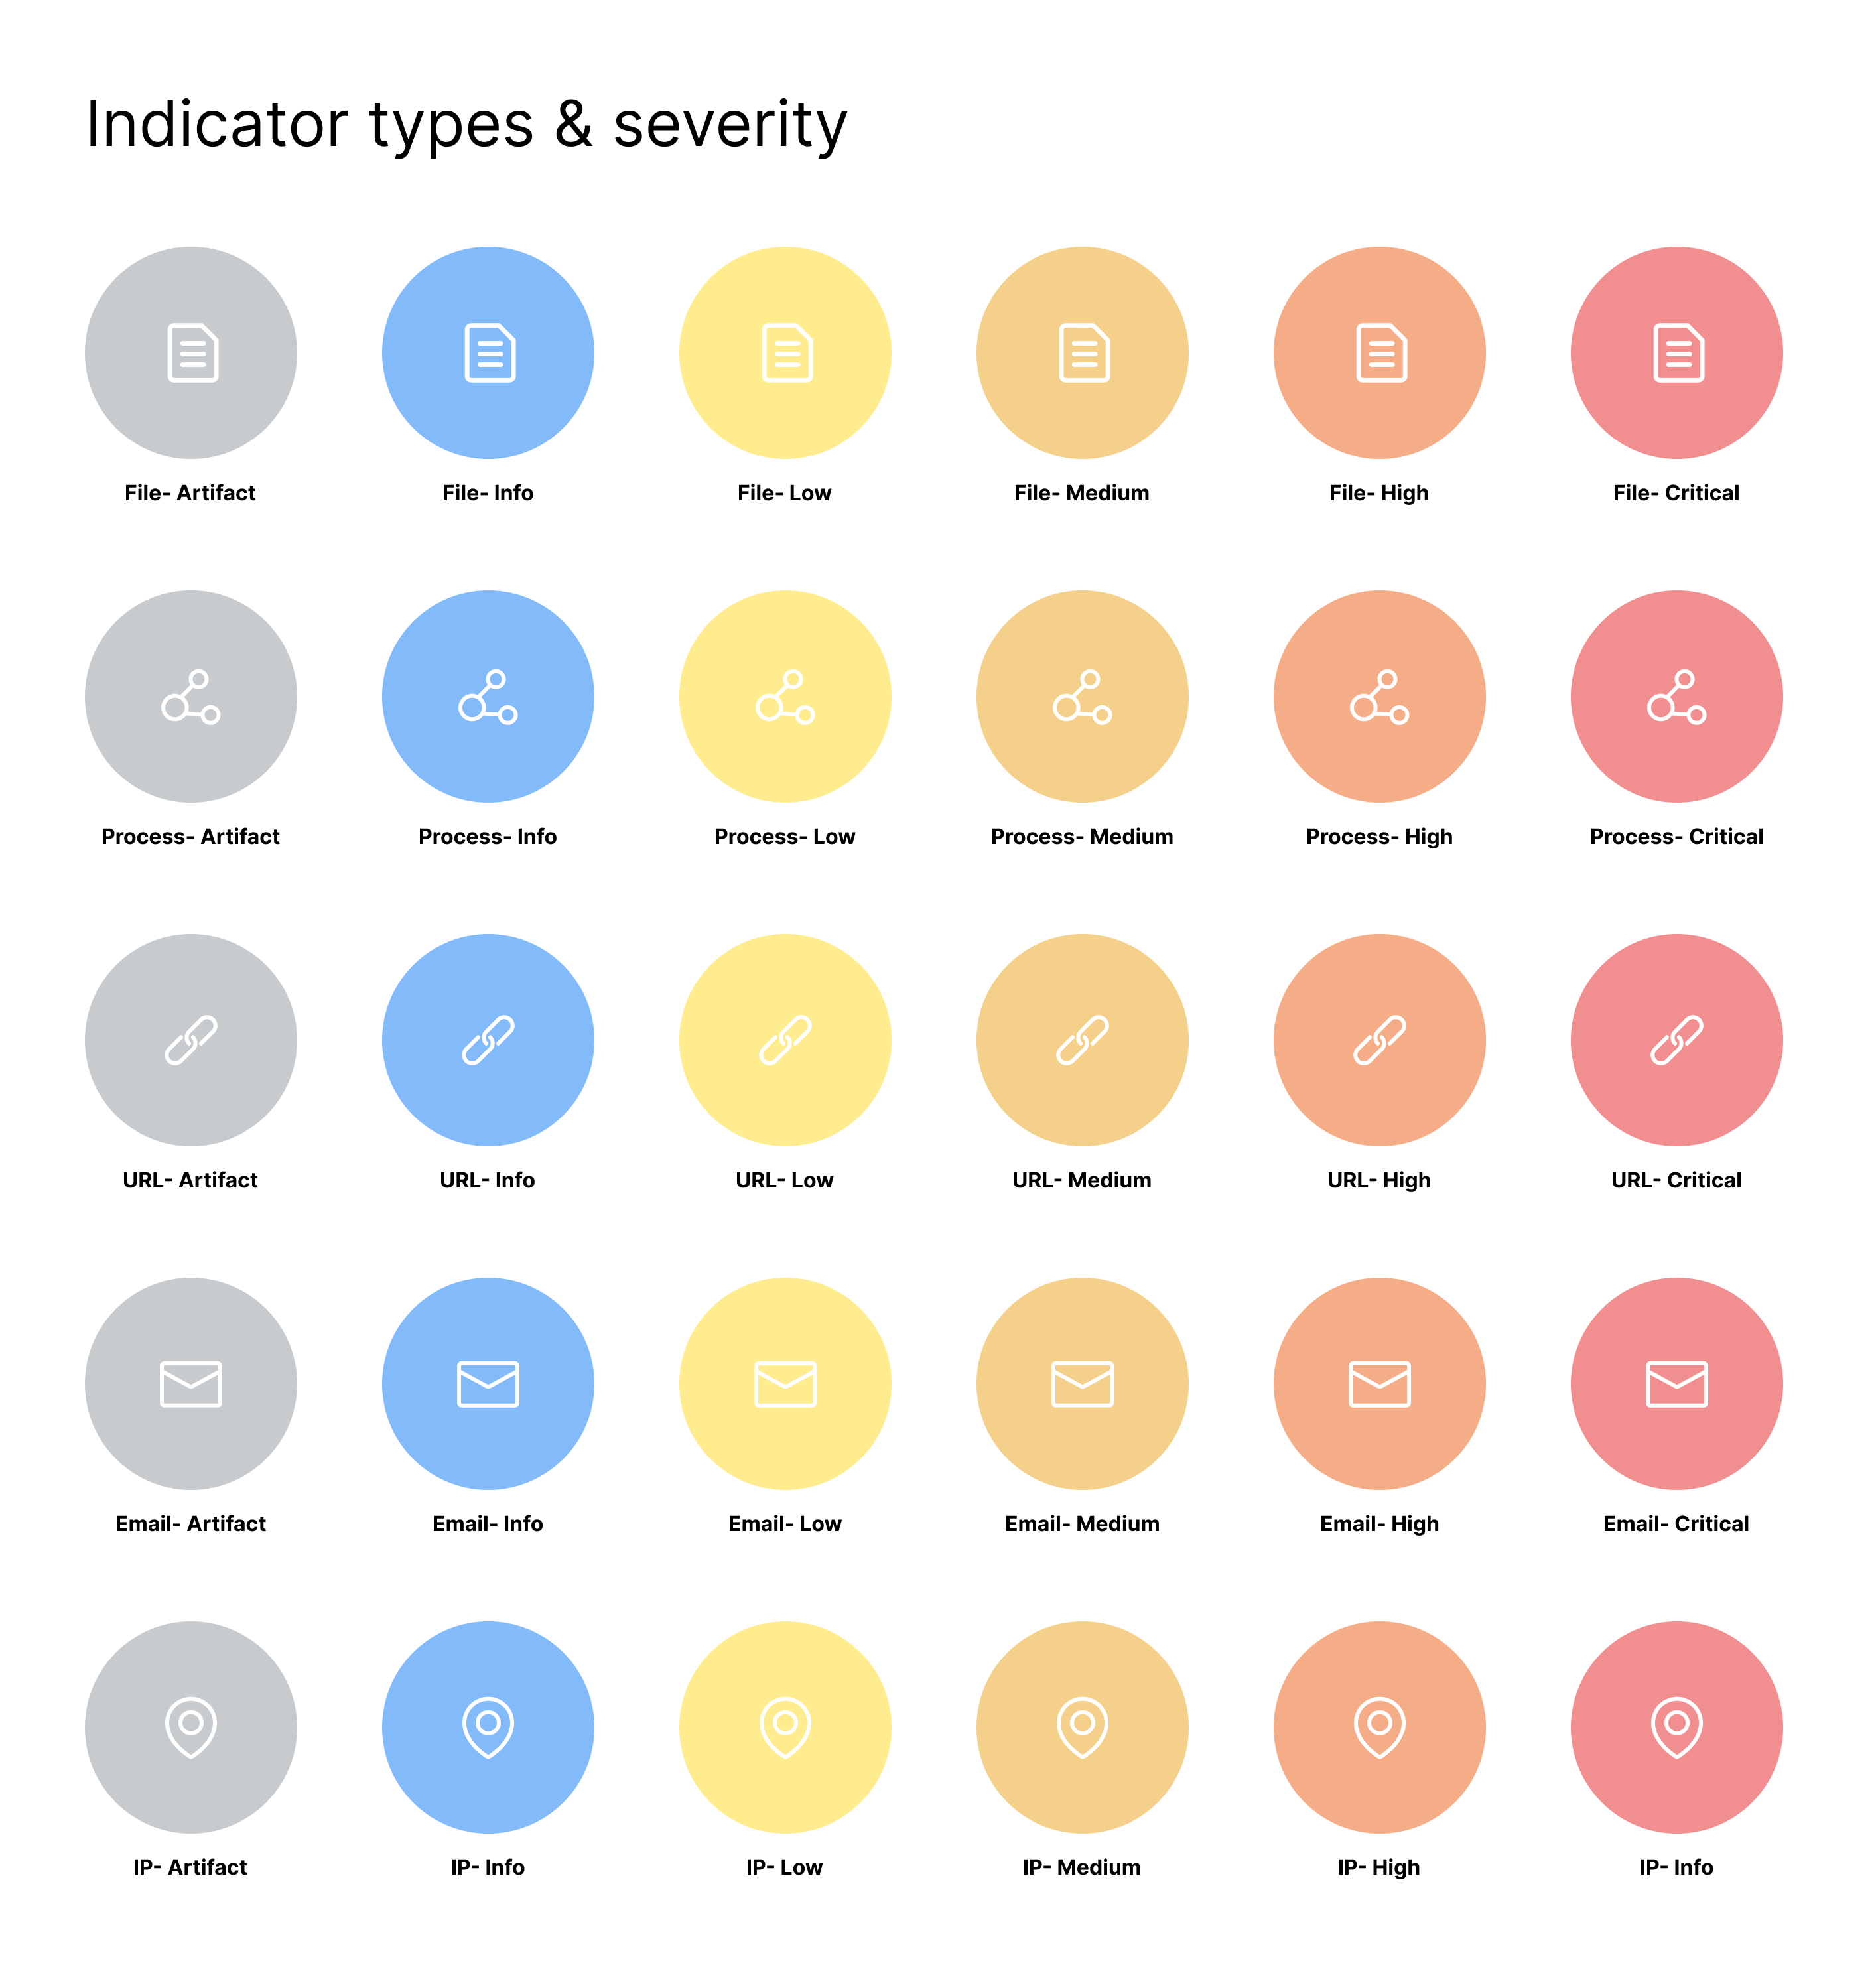
Identify entities
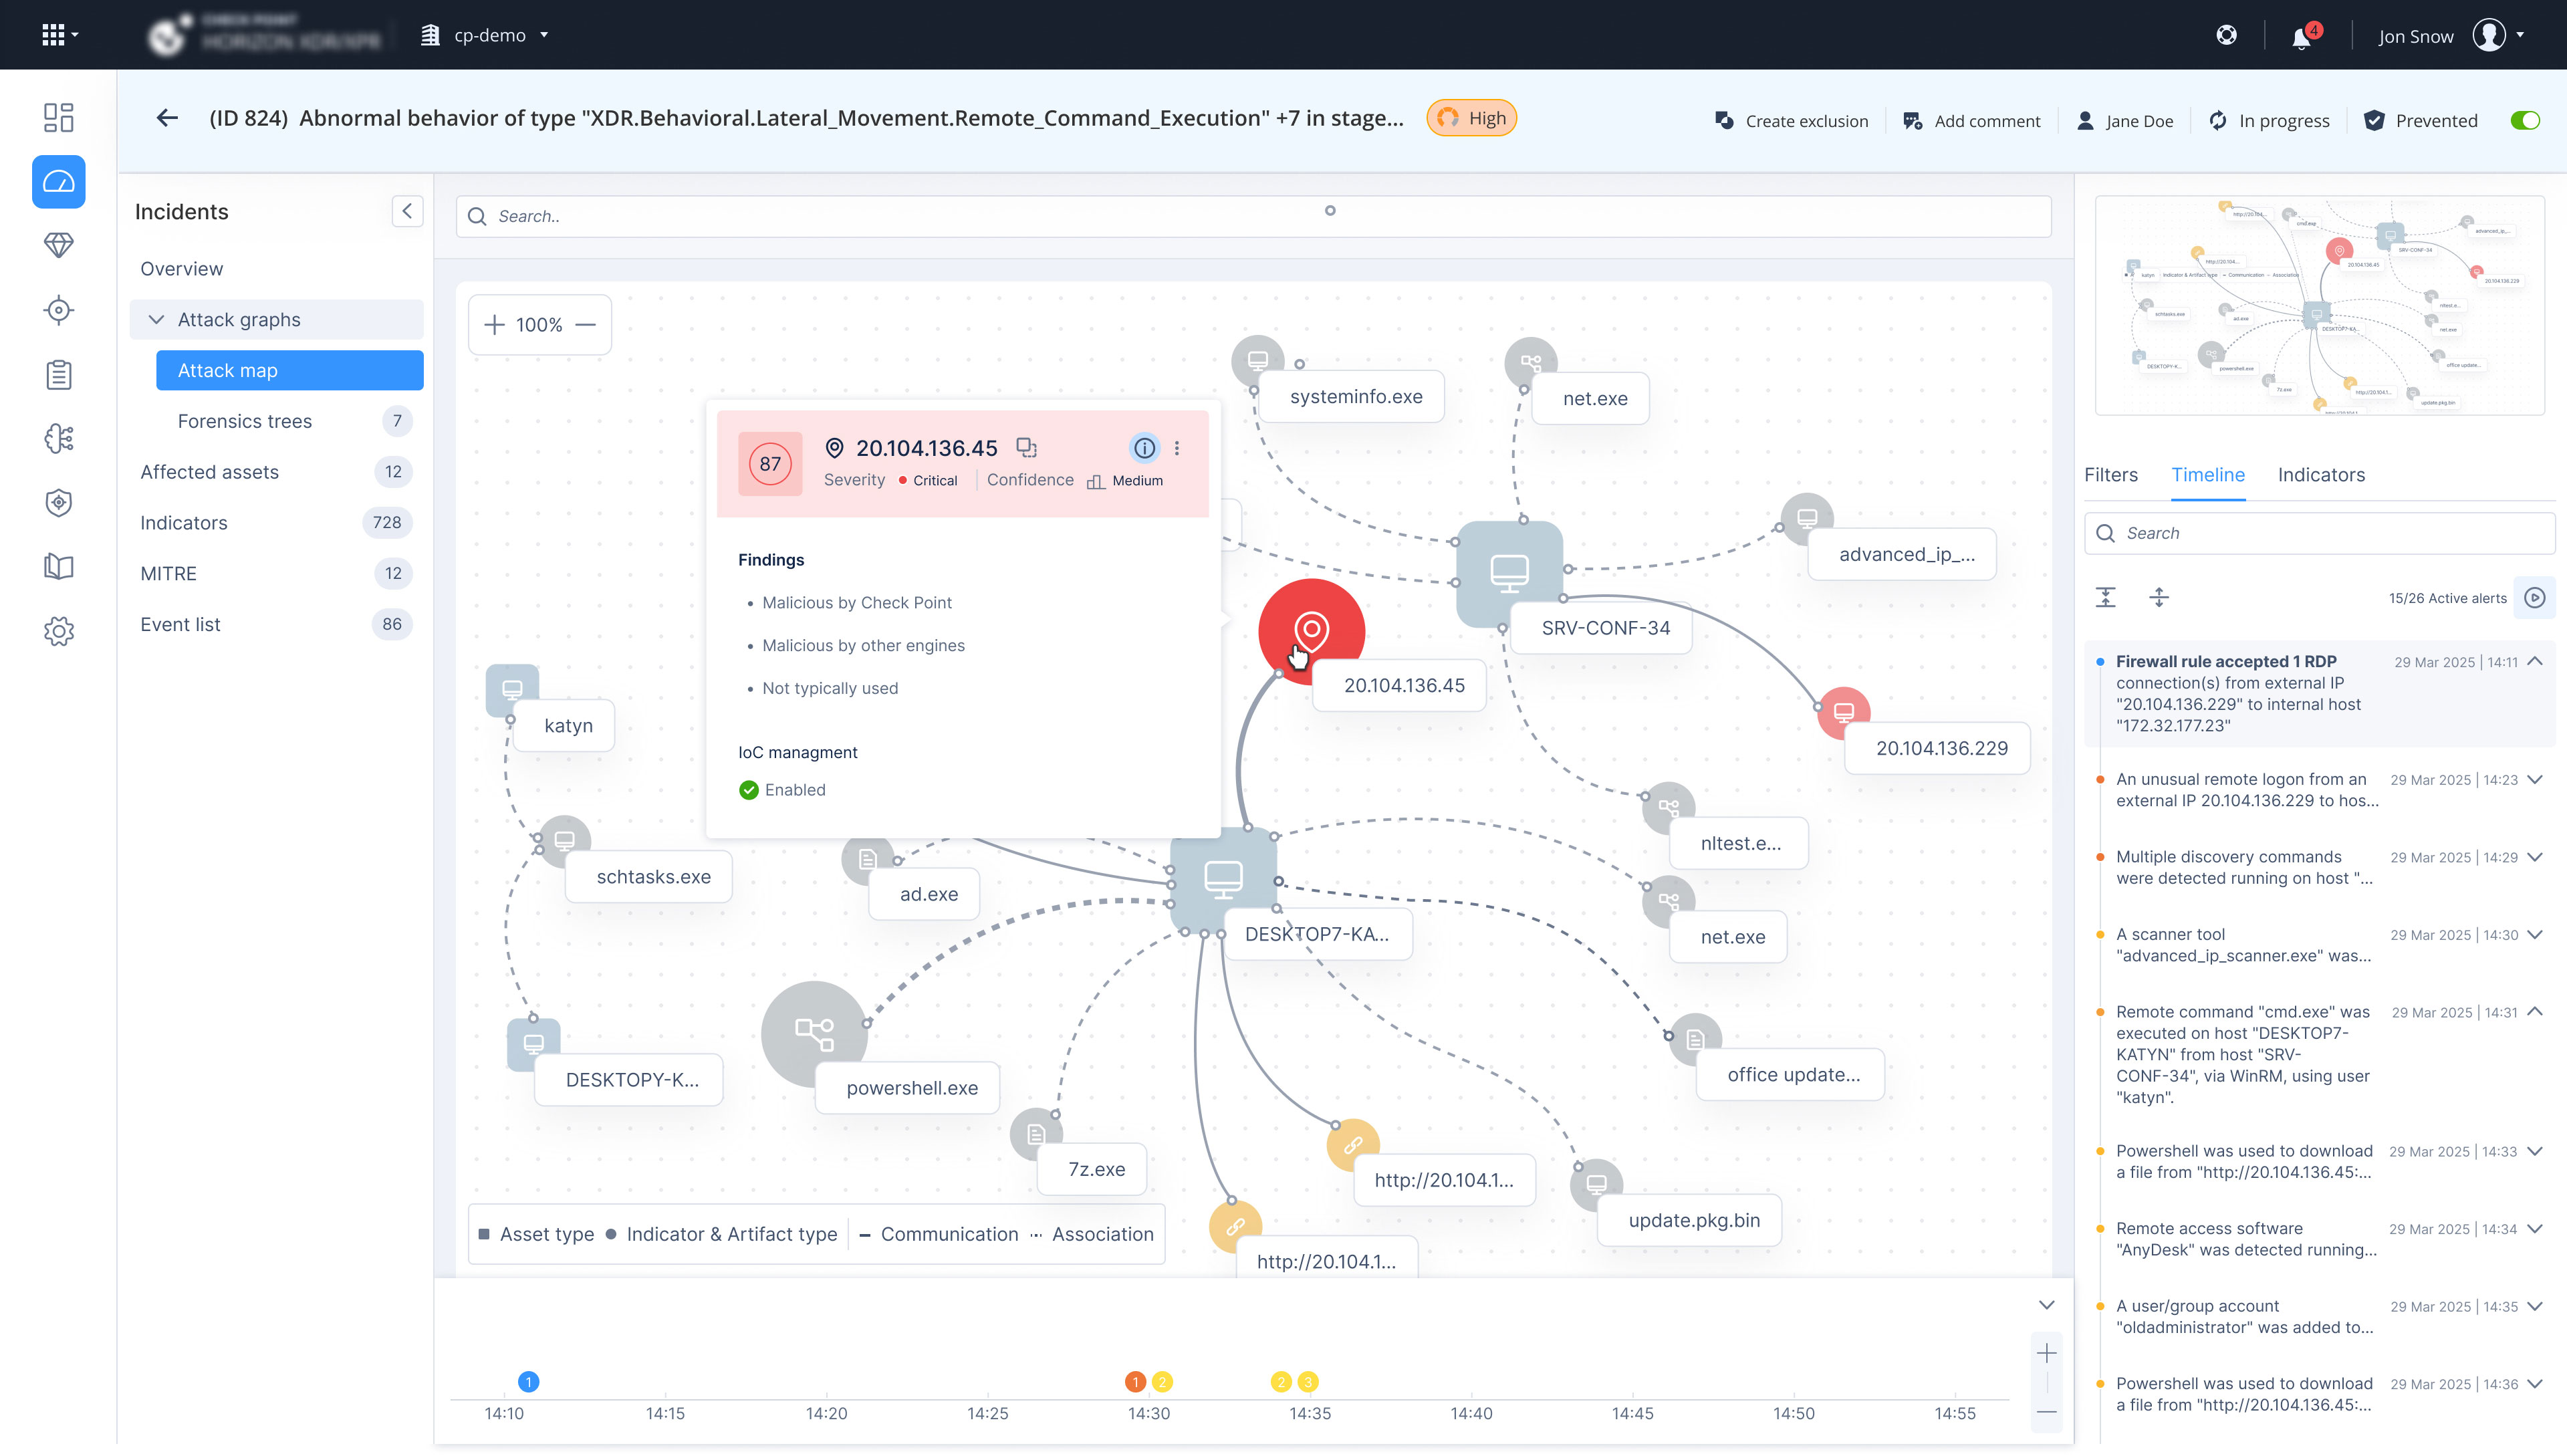
Use visual differences to distinguish asset and attack types.
- 04
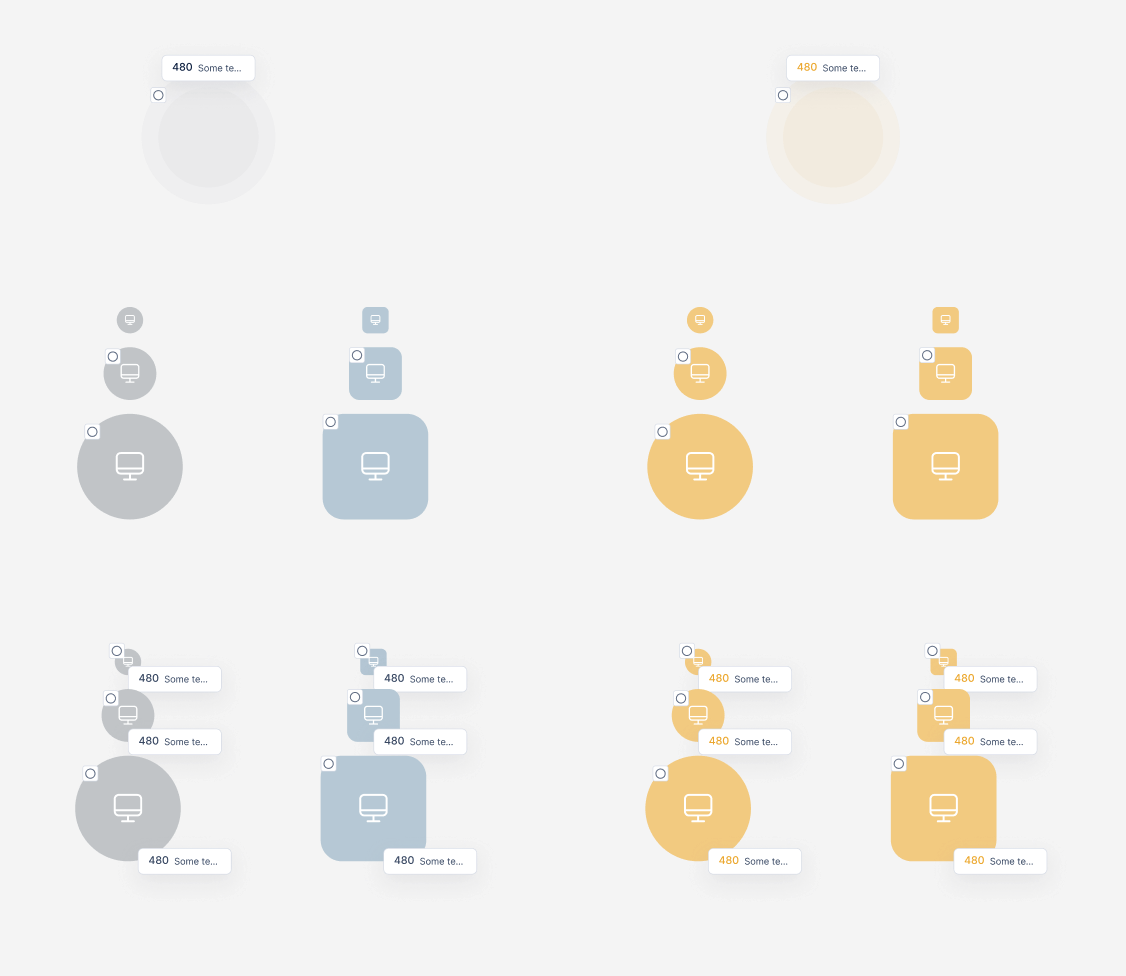
Group when helpful
Group dense maps and keep small maps readable without extra steps.
- 05
Inspect a group
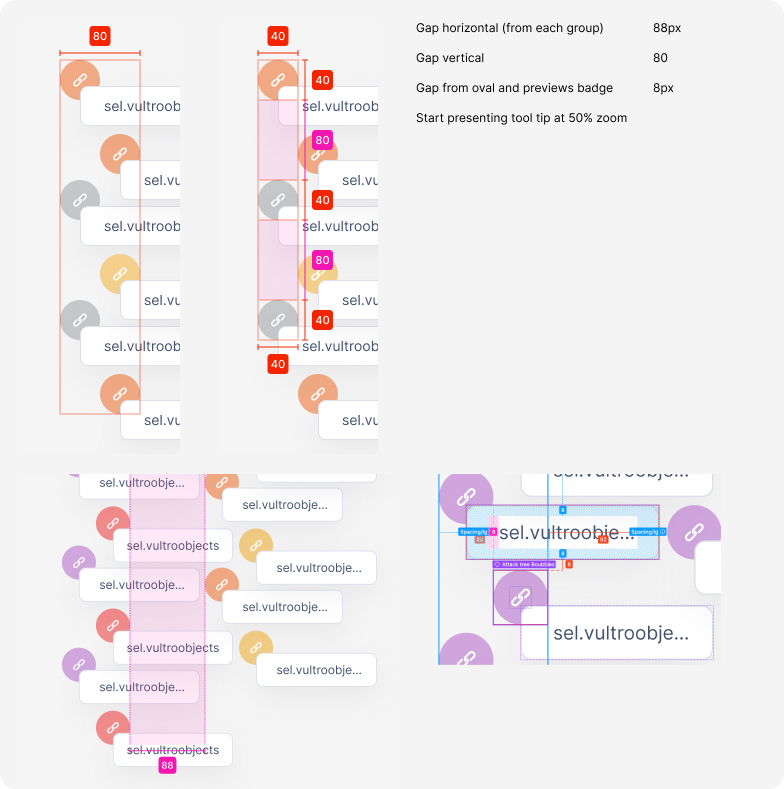
Expand a group to see its contents in context.
- 06
Continue investigating
Follow contextual links to examine the entities in more detail.
Inside the experience
product design detail 1
product design detail 2
product design detail 3
product design detail 4
product design detail 5
product design detail 6
product design detail 7
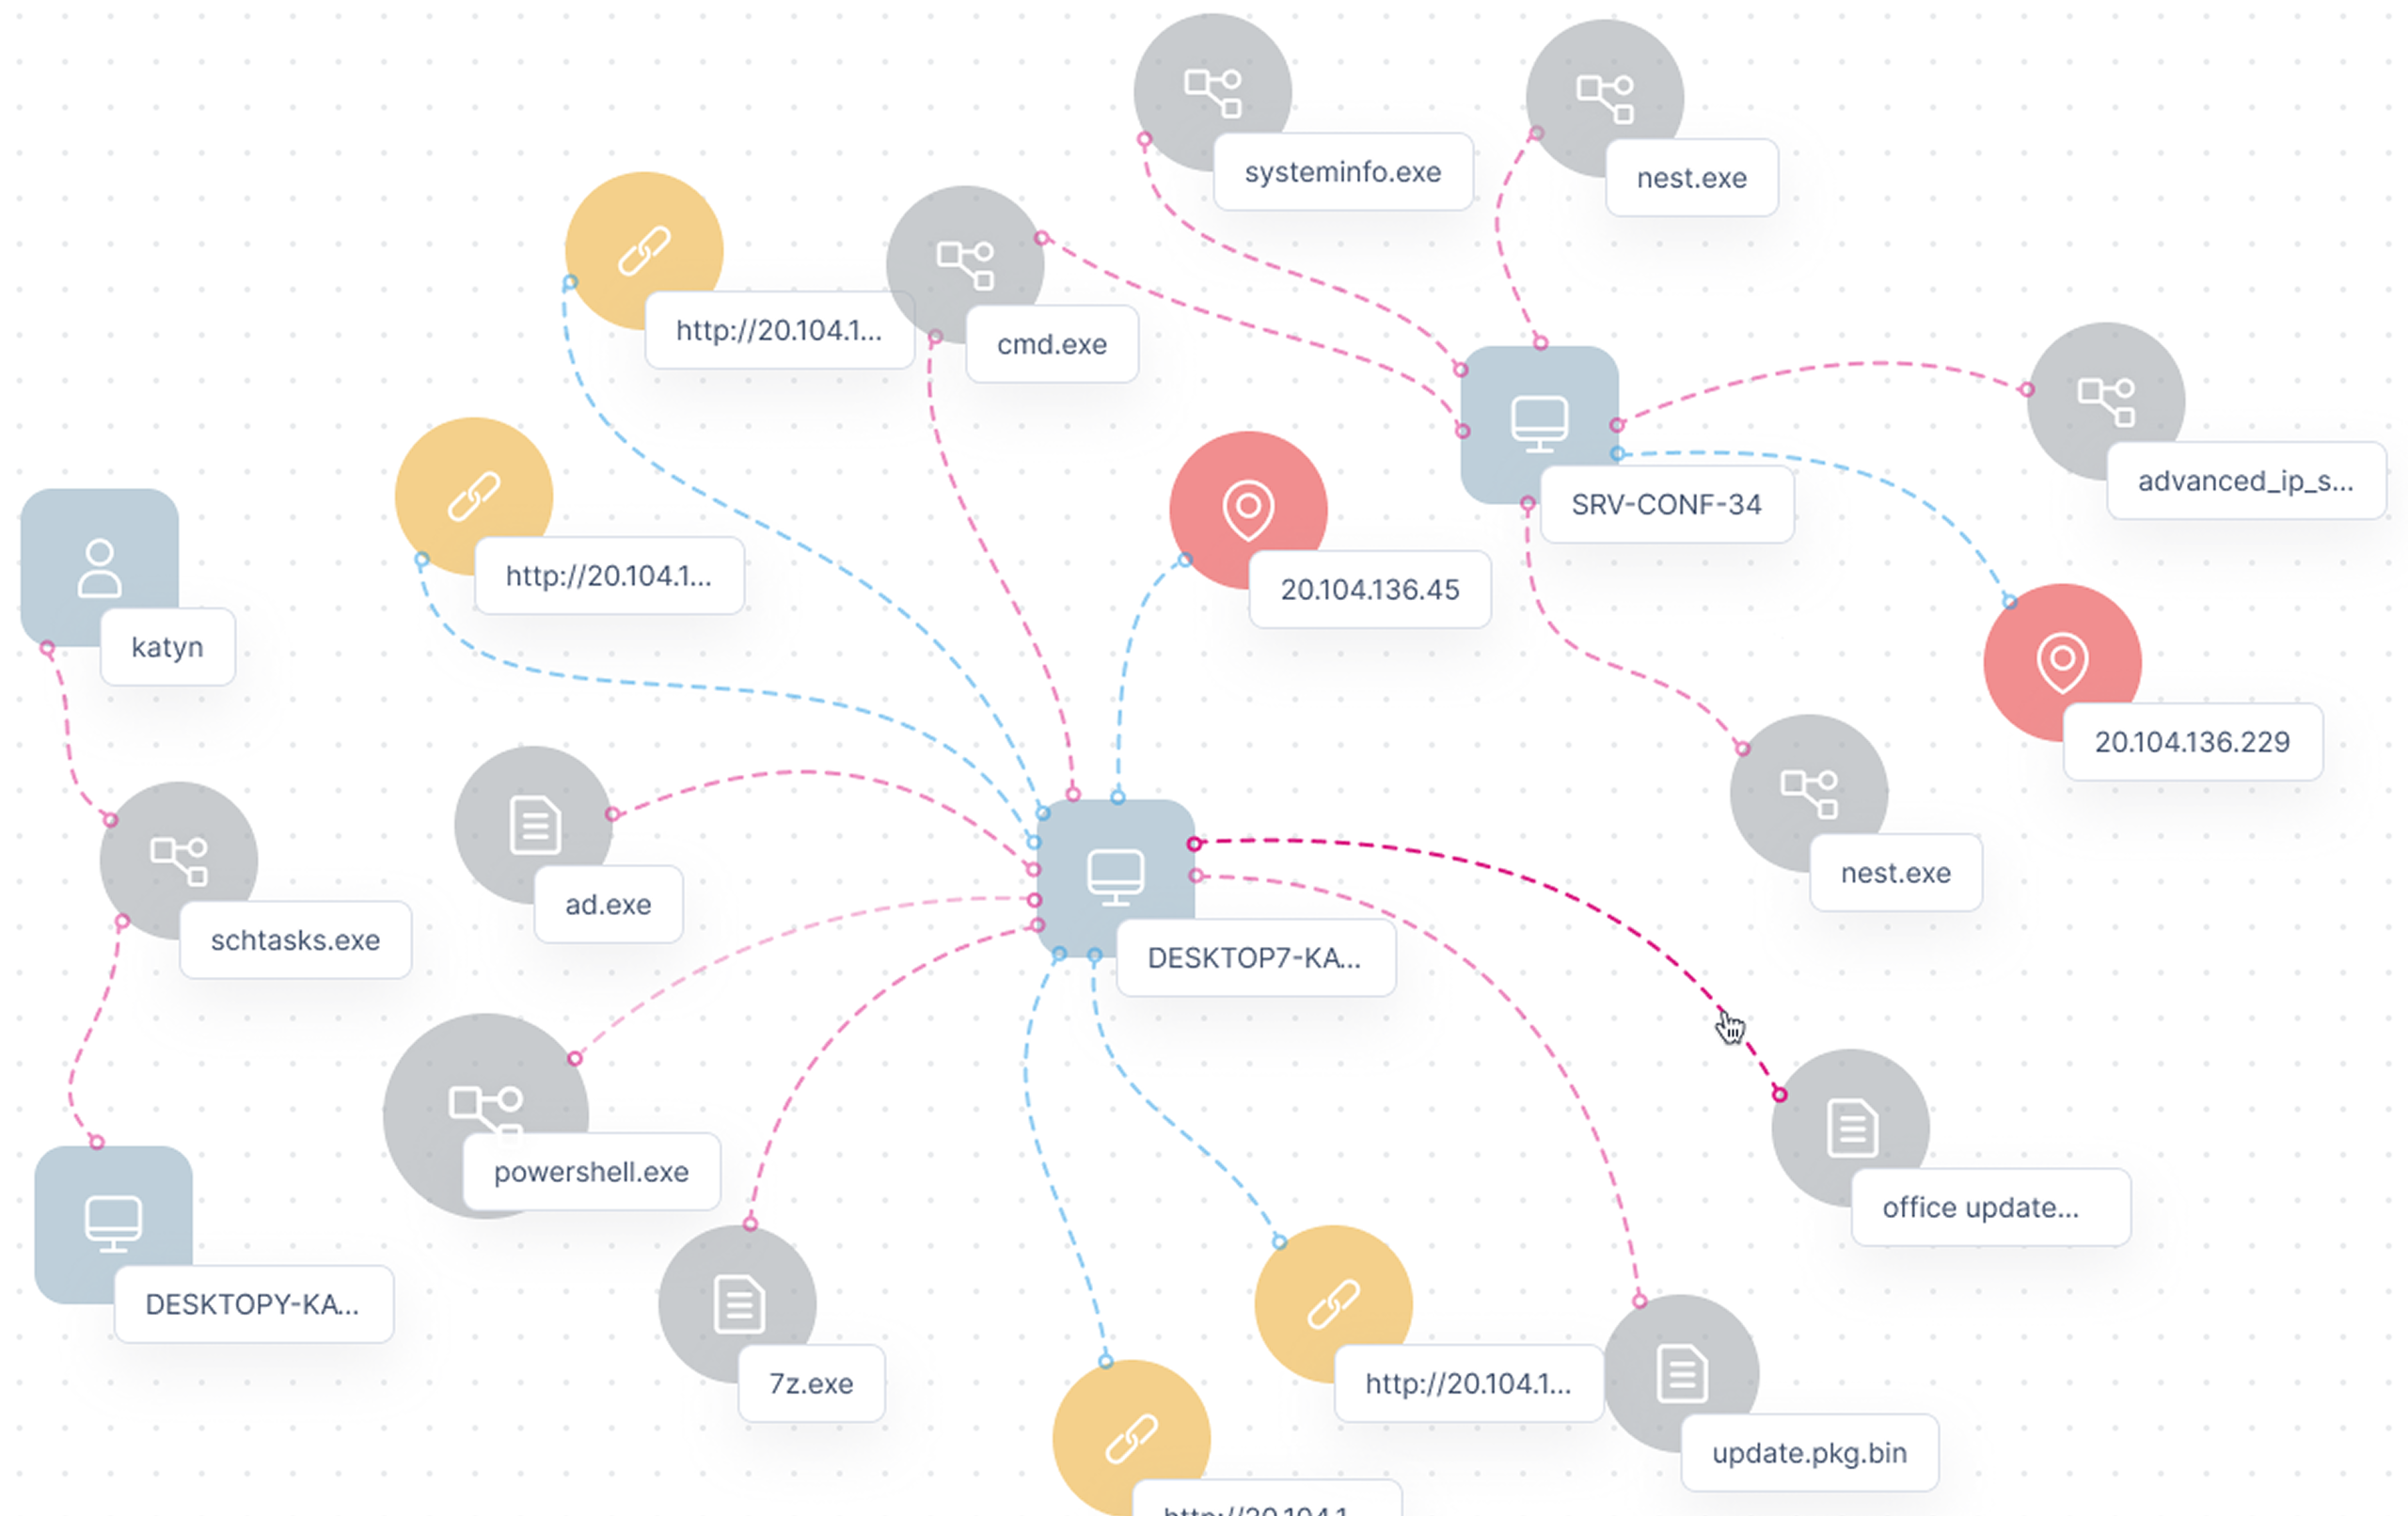
What the flow makes clear
Optional grouping makes dense maps easier to read while keeping small investigations direct.
More selected work
Let’s work together
Open to fully remote product design roles and selected digital projects.
Phuket, Thailand · Fully remote · Israel business hours